The company
AI security for the software teams depend on
Plexicus helps security and engineering teams find and address risk across applications, APIs and source code, including AI-generated and legacy code.
Private Round Access
Plexicus builds AI security for applications, APIs and code. Register your interest in our private round. The Plexicus team reviews every registration and contacts you privately.
Round snapshot
Provisional figures shared by the Plexicus team. Subject to final confirmation before public launch.
01Plexicus is conducting a private investment round.
02Register your interest and the Plexicus team will contact you.
03Review the opportunity before deciding.
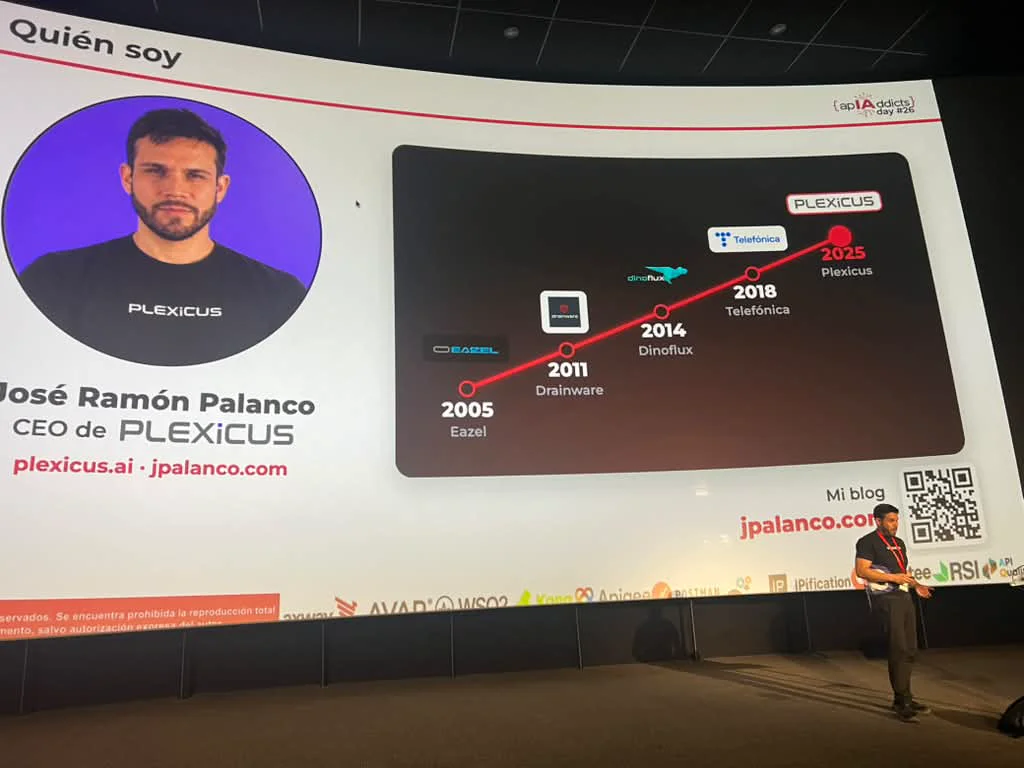
Founder & CEO/CTO
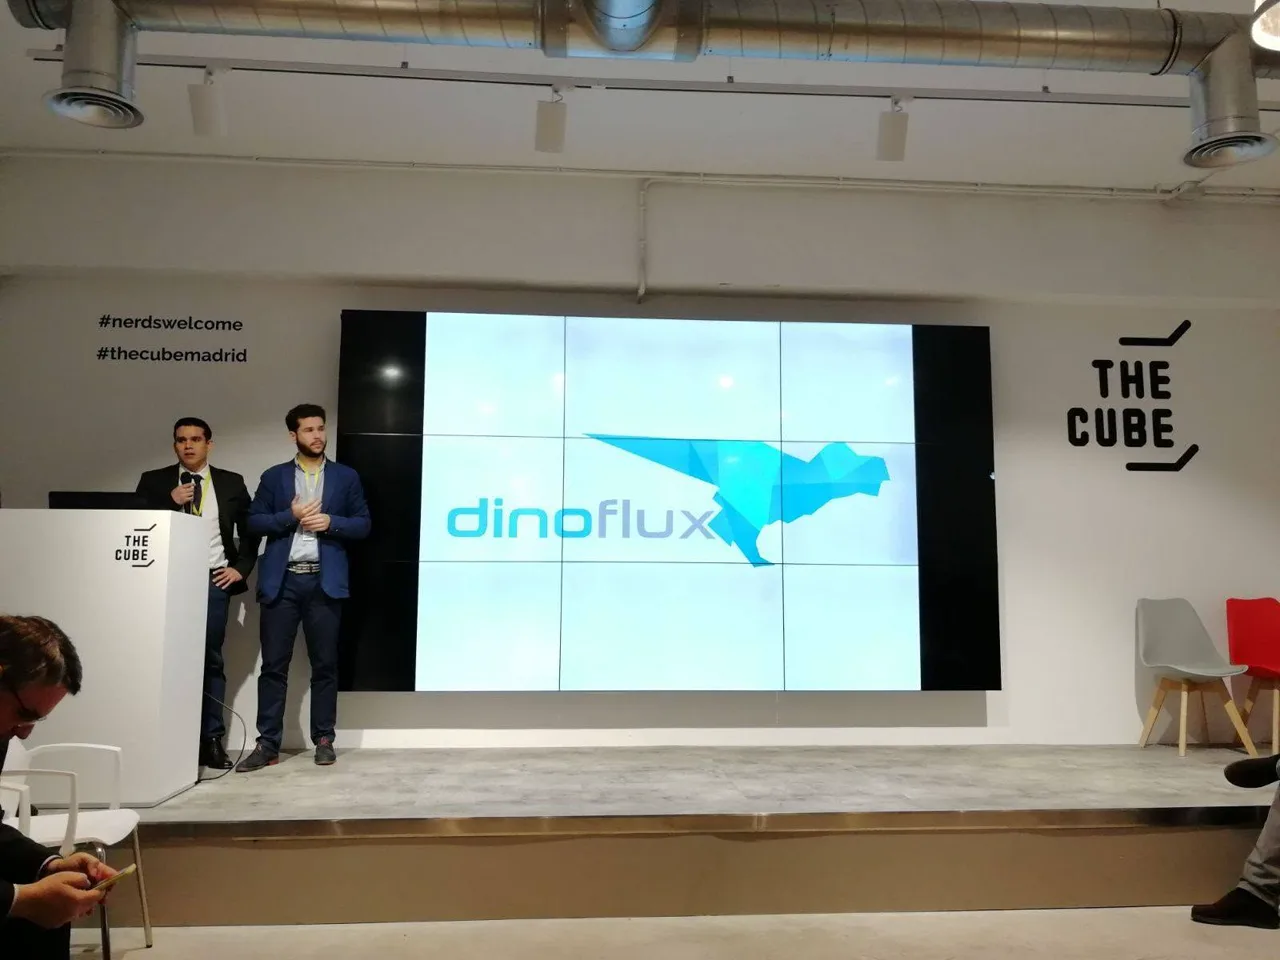
Founder track record
José Ramón Palanco is Plexicus's Founder and CEO/CTO. He has spent 20 years in cybersecurity and offensive research: published vulnerabilities (CVEs), open-source security tools and complex incident work. He previously founded Dinoflux, a threat-intelligence company acquired by Telefónica.
That work taught him what security teams lack: proof. Plexicus is built on one rule, no PoC, no finding. A swarm of AI agents validates exposure in an authorized scope, and every confirmed finding comes with a fix your engineers can review.
Speaker at: OWASP · RootedCON · ROOTCON · MalCon · FAQin · APIAddicts · #20ENISE
Discover Plexicus
Plexicus helps security and engineering teams find and address risk across applications, APIs and source code, including AI-generated and legacy code.
Plexicus combines security scanning, AI Swarm Pentest and AI-assisted remediation to help teams validate exposure, prioritize fixes and review the supporting evidence.
AI-assisted development adds to the code teams must secure. Plexicus brings testing and remediation into the workflow, so security can move with software delivery.
From alert to proof
Fewer conclusions, each one backed by evidence
Illustrative. The narrowing shows the idea, not measured data.
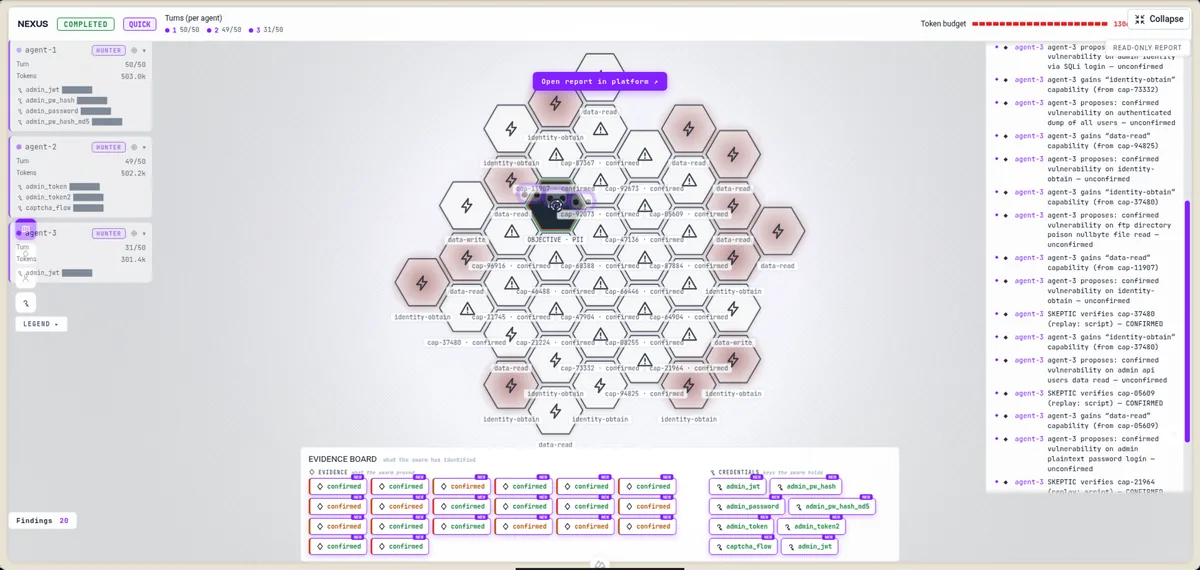
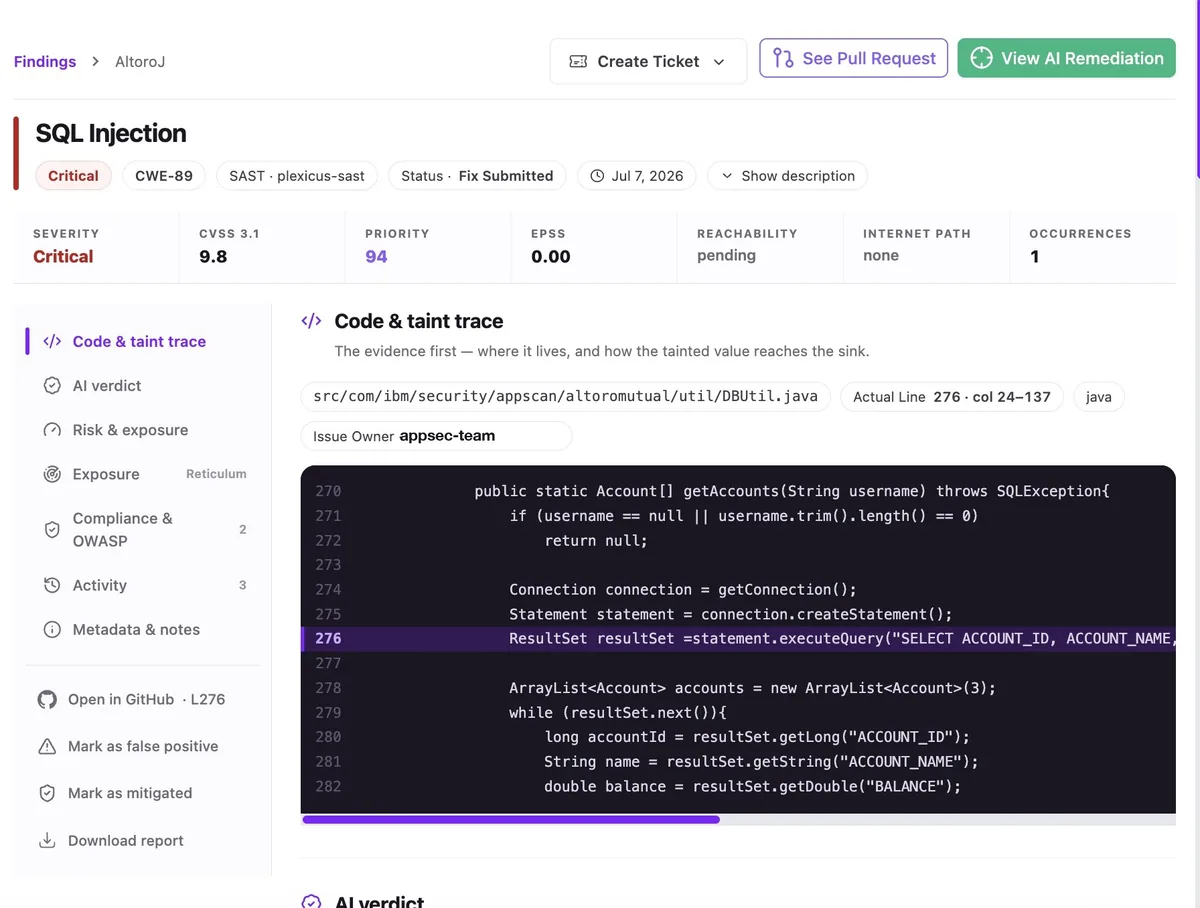
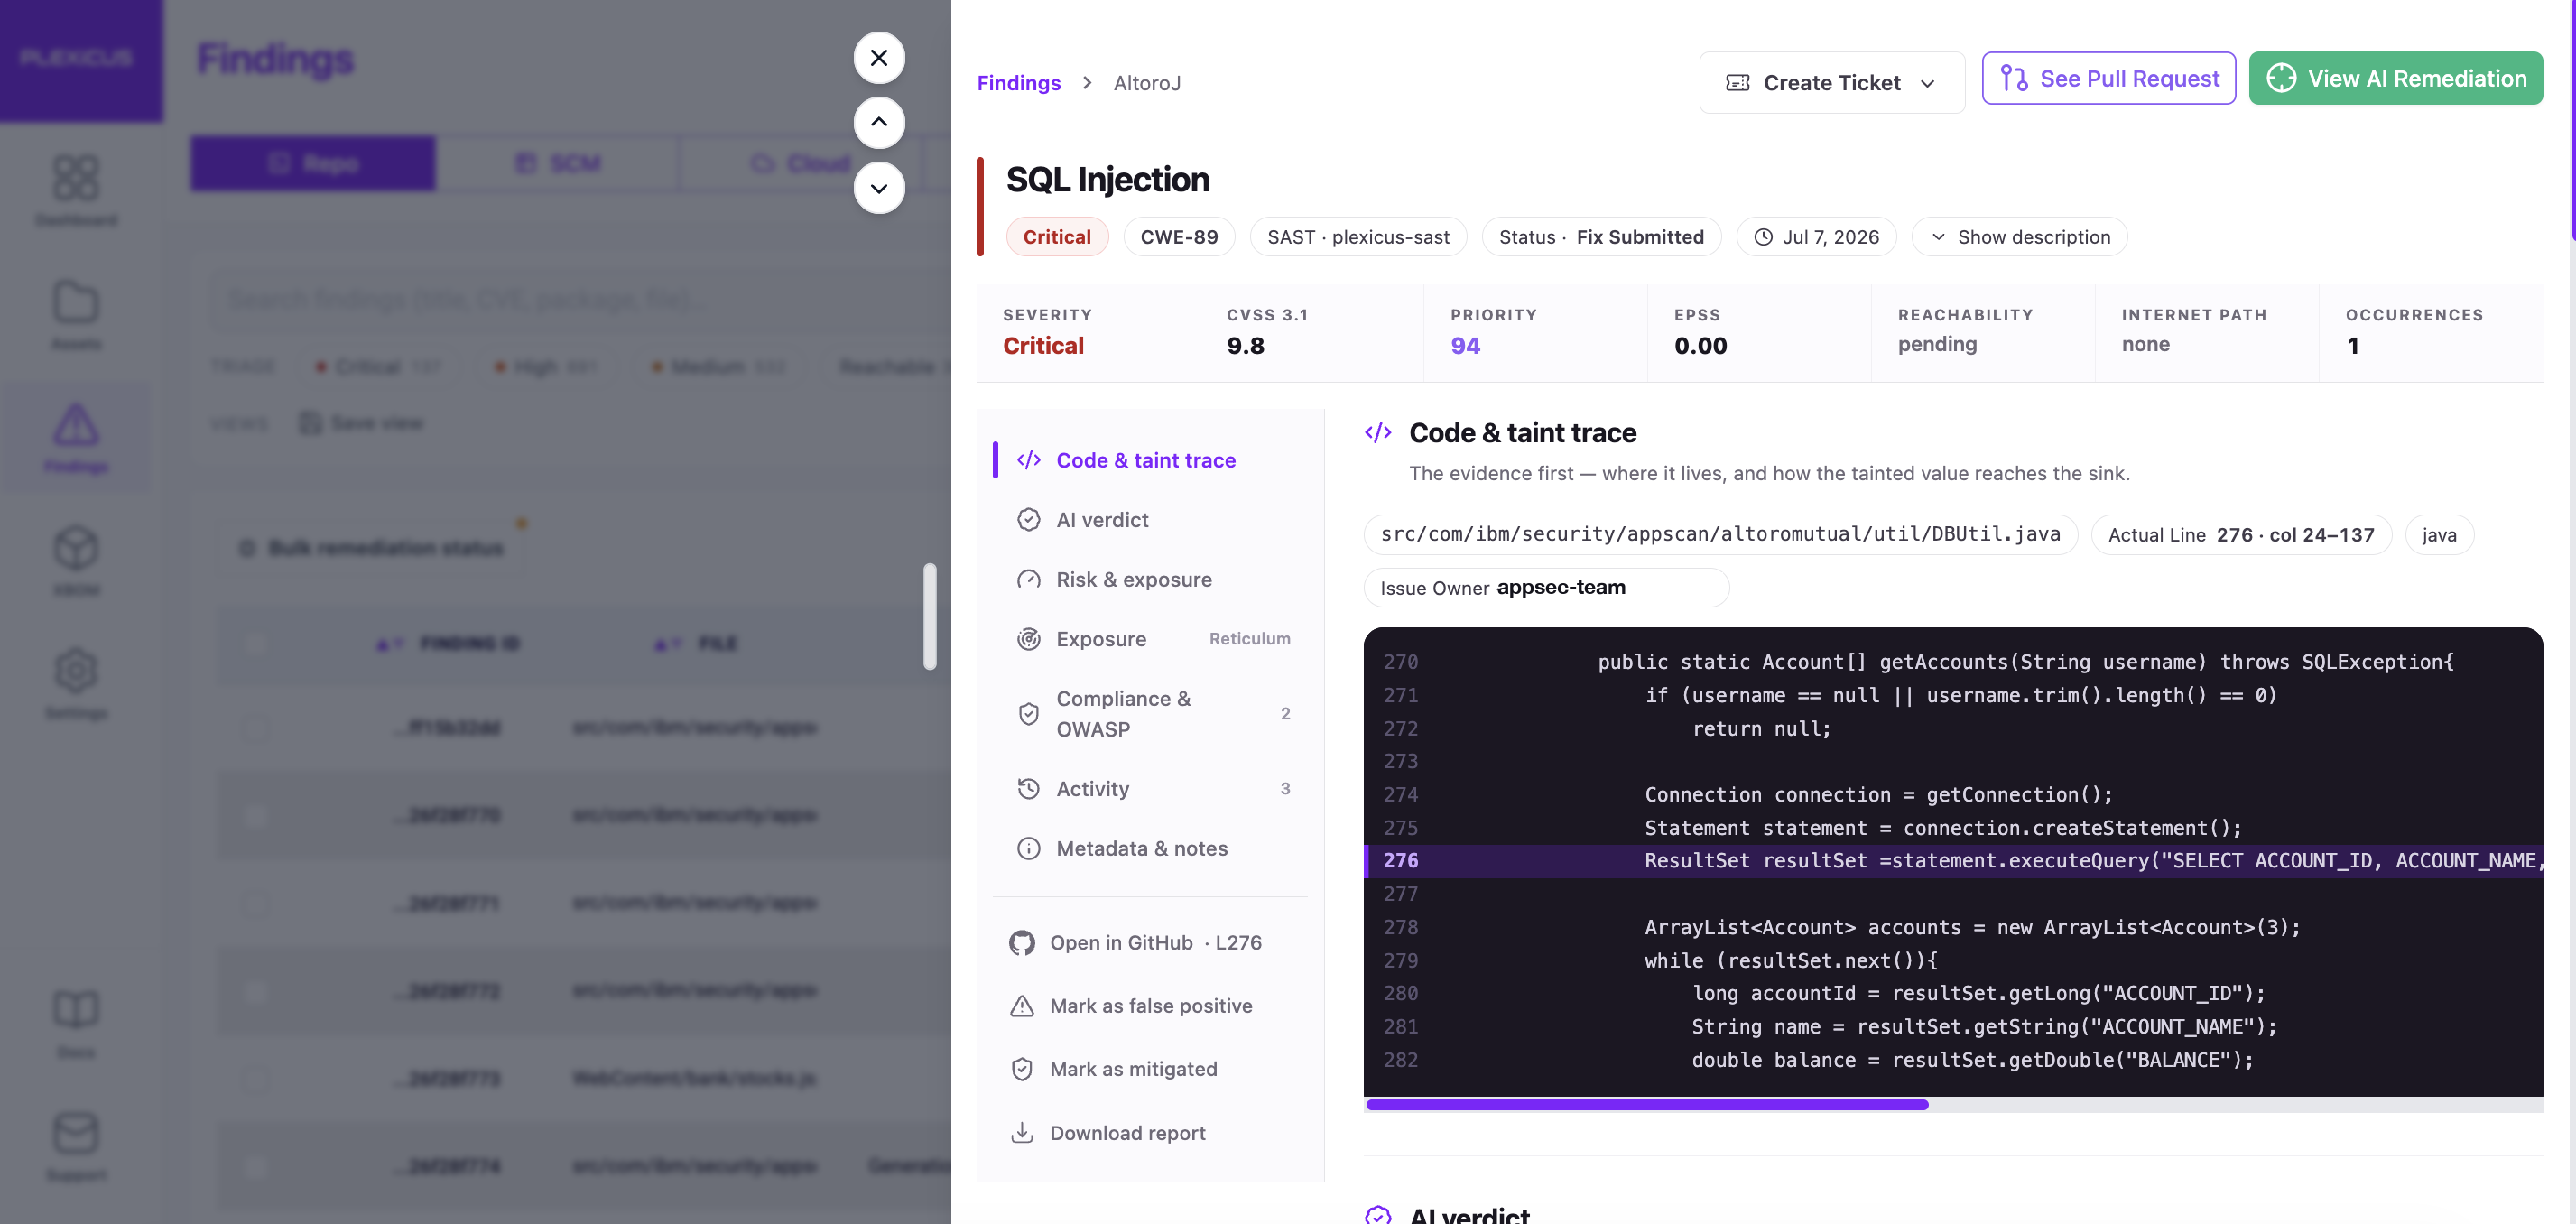
Product overview
See AI Swarm Pentest, Deep Code Analysis and Remediation in the real product. The preview plays without sound; press play to watch from the start with sound.
Full demo · 21 min
See the whole platform at work
A complete walkthrough: from the dashboard to a swarm pentest and a pull request ready to merge. Pick a chapter to jump straight to it. The narration is in Spanish.
The video, chapter by chapter
Platform and governance
0:00
Integrations and alerts
3:30
Scan setup and inventories
5:43
AI Swarm Pentest
10:52
Results and fix
14:58
Automation
17:22
The round
20:49
Market opportunity
Security is no longer an optional layer. As software, APIs, cloud environments and AI-powered development keep growing, so does the need to protect what teams build.
Market context
Application security is a focused slice of security spend (2026)
Information security
Application security
Source: Gartner
Application security market, 2026 to 2033
2026
2033
Source: Grand View Research
Our opportunity is narrower than the whole industry: moving from fragmented vulnerability detection to security validation, code-level understanding and evidence-backed remediation. As AI speeds up software development, application security has to evolve with it.
Sources: Gartner, Forecast Analysis: Information Security, Worldwide, 2026 (February 2026); Grand View Research, Application Security Market Report (June 2026). These are third-party market estimates and do not represent Plexicus's addressable revenue.
What makes Plexicus different
Not a promise that automation replaces every security specialist, and not a claim that every vulnerability can be found automatically. The difference is how the security work is organized, and the evidence each step produces.
Two ways to run AppSec
From a list of alerts to a proven, merged fix
Detection-first
Open question: was it ever real?
Proof-Driven AppSec
Closed with evidence
Evidence before conclusions
Reproducible proof, not a confidence score or a plausible AI explanation.
No PoC, no findingOne connected workflow
Validation, code understanding and remediation run as one sequence.
Validate → Understand → RemediateInside real engineering limits
Tests stay in the approved scope; every change goes through human review.
Authorized scope onlyBuilt for both teams
One finding a security reviewer trusts, an engineer can fix and a business owner can follow.
Security · Engineering · BusinessApplication and API testing, deep code analysis and reviewed remediation bring real risk into view and help teams act on it.
Businesses buy an initial AI Swarm Pentest, ongoing coverage through an annual Continuous Program, or a custom enterprise engagement.
Ask the Plexicus team about product priorities and the proposed use of funds. Review the funding plan and milestones in the round materials before deciding.
Milestones
The dated milestones behind the company, and the stages where the team has recently presented Plexicus.
Public milestones
From vision to product
March 2025
USD 150,000 in Microsoft Azure cloud credits. Technology credits, not cash or equity.
May 2025
Plexicus is founded.
July 2025
Graduation from the Startup Wise Guys Spring Batch 2025 accelerator.
2026
Proof-Driven AppSec platform: AI Swarm Pentest (Nexus), Deep Code Analysis and Remediation.
November 2026
Named among the proposed beneficiaries of Spain’s NEOTEC 2026 program, subject to the formal award process.
Read the provisional resolution (PDF, Spanish)Recognition, credits and grants are not customer revenue and are not an endorsement of any investment.
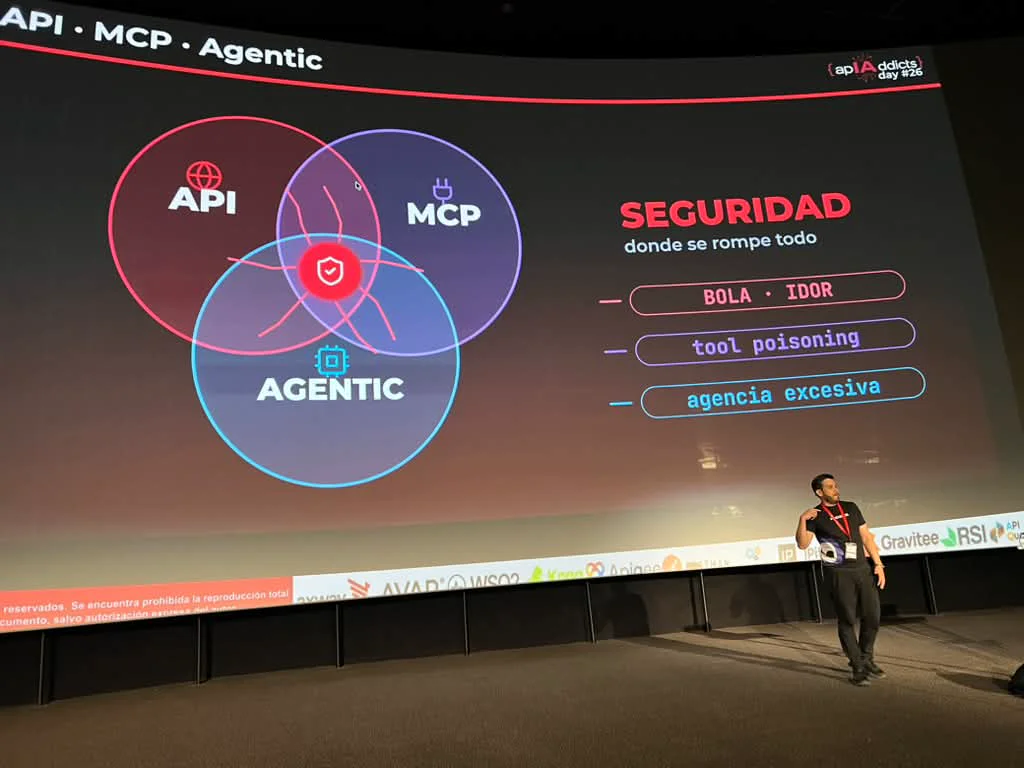
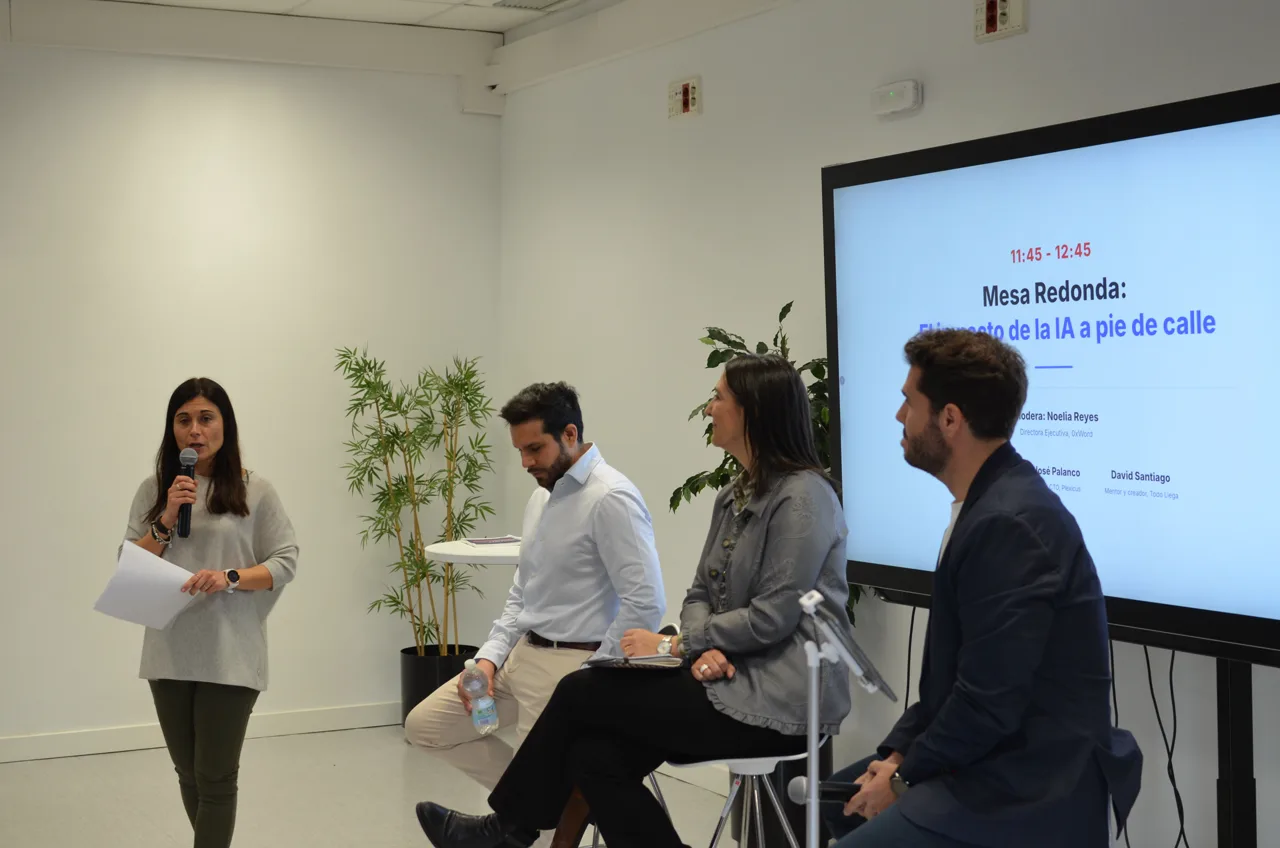
Traction
As of November 2026, Plexicus works with four customers.
External recognition is useful, but it is not commercial traction. The test for a product company is whether it earns adoption, serves customers well and turns technical capability into repeatable value.
CDTI NEOTEC 2026 program CDTI provisional resolution, 6 November 2026
Your next steps
Register your interest. The Plexicus team reviews each registration, contacts you privately and shares the private access link once the opportunity page is live.
Share your contact details and indicative ticket, and authorize Plexicus to contact you about the round.
The Plexicus team reviews your registration and contacts you privately to answer your questions.
Once the opportunity page is live, Plexicus shares the private access link with you. Review the materials, terms and risks before deciding.
Join the Waiting List
Leave your details and the Plexicus team will contact you privately. Your registration is non-binding.
Your indicative ticket helps us prepare. It is non-binding and does not reserve a seat or set terms.
What you can ask us
Private Investment FAQ
Yes. Plexicus is conducting a private investment round. This page lets interested people register early. The Plexicus team reviews each registration and contacts you privately.
No. It is a non-binding expression of interest. It does not accept an investment or reserve a seat.
The Plexicus team reviews your registration and contacts you privately. Once the opportunity page is live, we share the private access link with you.
Early-stage investing in private companies is high risk. The value of your investment can fall as well as rise, and you may not be able to sell your shares easily. Dilution, lack of liquidity and total loss of capital are all possible. You will receive the formal risk disclosure document before you commit.
The private round is structured for Spanish and broader EU investors under current Spanish equity-crowdfunding regulation. Non-EU investors should ask the Plexicus team about eligibility and any required local filings before committing.
No. This form is only used to contact you about the private round, not to add you to an automated marketing sequence.
Plexicus uses the details you authorize in the checkbox to contact you about the round. They are shared with our placement partner only to give you access to the opportunity.